
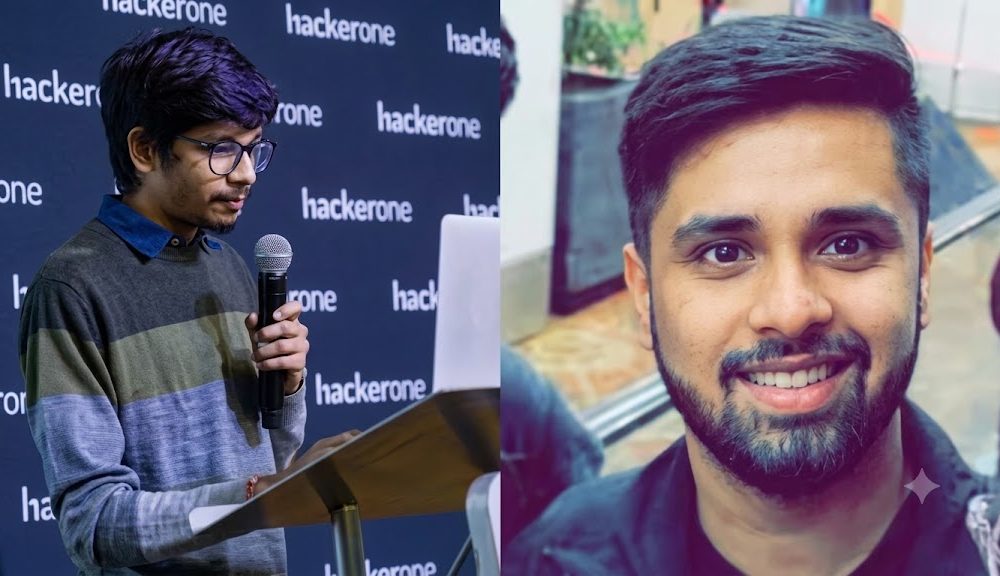
Three Indian-origin cybersecurity researchers from startup Hacktron AI used Anthropic’s Claude and other AI tools to identify and exploit vulnerabilities in OpenAI’s systems, gaining access to employee accounts and demonstrating a route into a private code repository, according to media reports.
Mohan Pedhapati, Harsh Jaiswal and Rahul Maini were testing OpenAI systems through its bug bounty programme. The team reportedly chained two vulnerabilities and reached internal systems in less than 72 hours.
The researchers began by examining OpenAI’s community forum, which runs on Discourse, and identified a vulnerability involving image processing. Claude helped them develop working exploit code, allowing access to the forum’s environment.
They then identified a weakness involving OpenAI’s single sign-on system and obtained authentication information linked to employee ChatGPT and Codex accounts. One compromised account provided a route into OpenAI’s private GitHub environment.
The researchers demonstrated access to an internal repository by submitting a pull request but did not download or examine source code. OpenAI subsequently fixed the vulnerabilities and revoked the affected access.
The operation reportedly cost less than $3,000 in AI tokens, while OpenAI awarded Hacktron AI a $6,500 bug bounty.
Claude was not the only AI tool involved. The researchers also used OpenAI’s GPT-5.6 Sol for later stages, highlighting how human researchers are combining multiple AI systems in cybersecurity testing.